Managed SOC
What a managed SOC is: outsourced security monitoring, threat detection and incident triage, and what these services typically include.
Managed Security Operations Center (Managed SOC)
Outsourced security monitoring, threat detection and response.
Many organizations lack the internal resources or expertise to run a full security team around the clock. A managed Security Operations Center (SOC) provides continuous monitoring so that suspicious activity can be identified and investigated early. Providers typically combine analyst expertise with security tools, and organizations often consider it as an alternative to building an in-house SOC. Outcomes depend on the provider, the tools in place and how the service is scoped; no monitoring service can prevent every incident.
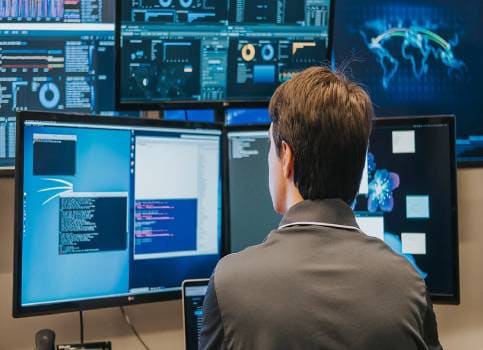
Typical features
- 24/7 monitoring and incident triage
- Threat detection using SIEM and threat intelligence
- Expert investigation and rapid response
- Monthly security reports and performance metrics
General information for learning only. It is not professional security, legal or compliance advice and does not guarantee any security outcome.
Keep reading
Managed OT SOC
What a managed OT SOC is: monitoring and response for industrial systems such as SCADA, ICS and IIoT.
Read the guide →
Incident Response
What incident response involves: containing a cyber incident, finding the root cause and supporting recovery, on demand or on retainer.
Read the guide →
Cyber Threat Hunting
What cyber threat hunting is: proactively searching for signs of compromise using human analysis, threat intelligence and MITRE ATT&CK.
Read the guide →